


Rakuten Securities disclosed possible exposure of customer data held in a test environment on November 17, 2026. Check your individual notification through the official service and review your login security. The company has not confirmed leakage of passwords or PINs, or related unauthorized trades, in the announcement reviewed here.
Checked November 18, 2026 (JST). This is the English edition of our customer guide. The official announcement does not establish a connection to the separate KARTE incident.
What information may have been exposed?
| Reported account figure | Potentially exposed information |
|---|---|
| Up to about 11.25 million | Branch/customer codes and Rakuten Securities login IDs. |
| Up to about 4.47 million | The above identifiers plus names, date of birth, address, phone, email, employer, withdrawal bank details, declared income/financial assets, assets by product and last login date. |
These are account counts, not confirmed numbers of individual victims. Do not add the figures together. Former customers are included. Rakuten Securities says the login IDs are different from Rakuten IDs.
The official announcement says possible unauthorized access was detected November 16 and information in a test environment may have been exposed November 11. Identification of affected customers was complete, with individual notification planned. The cause remained under investigation.
How to check your individual notification safely
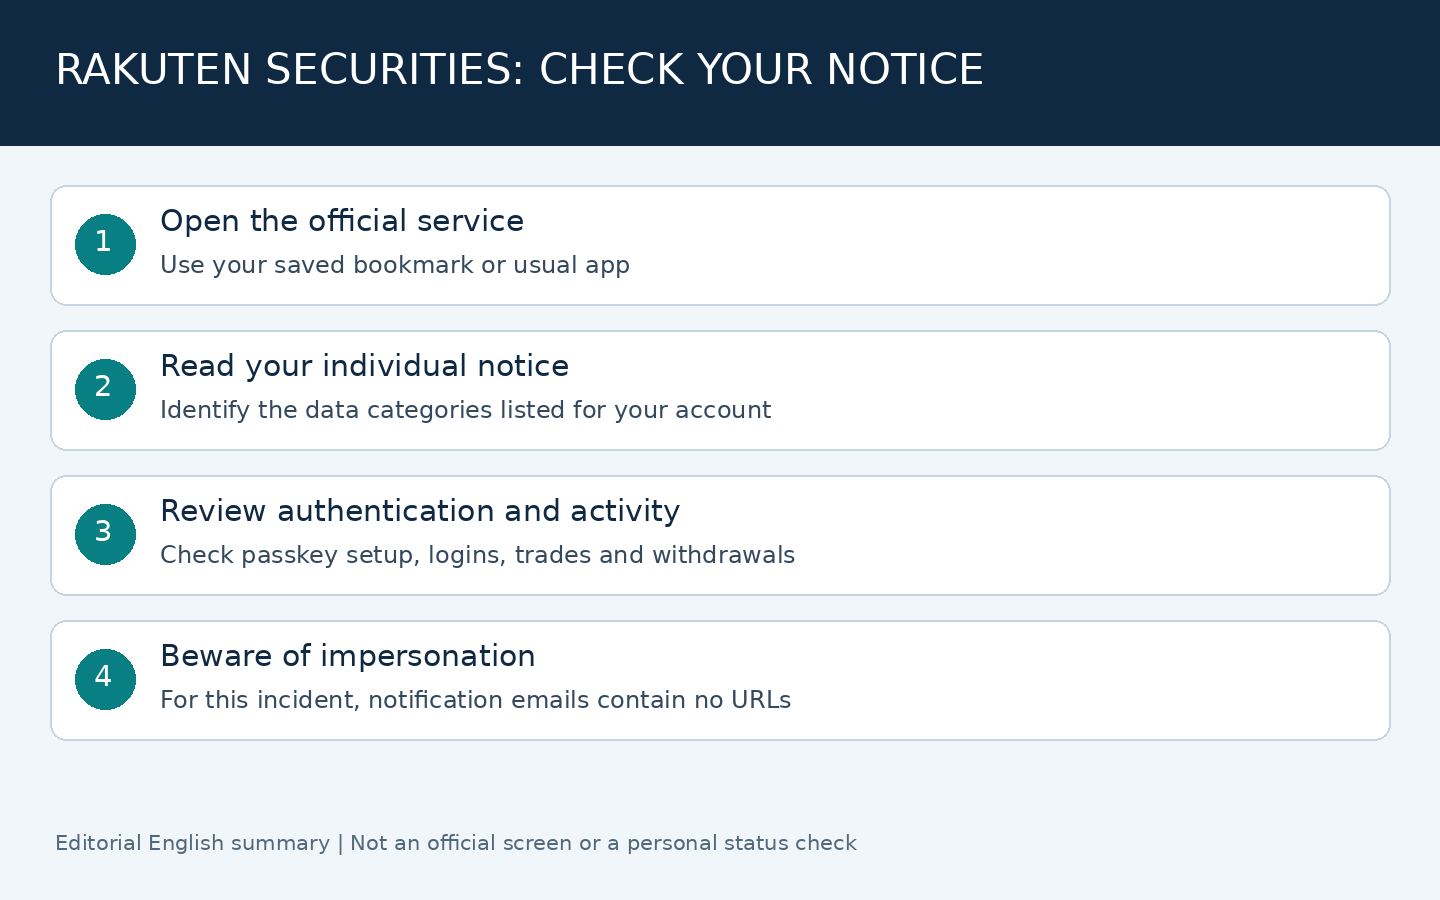
- Open your usual Rakuten Securities app or a saved official bookmark. Locate the company’s November 17 announcement and any personal notification.
- Compare the information categories in your notification with the public announcement. A public notice is not a personal affected-status lookup.
- Keep the notification privately with its receipt time and the listed data categories. Do not post identifiers or account details on social media.
- If the scope is unclear, contact support using the contact information on the official website. A missing notification alone is not proof that your account is unaffected.
For this incident, Rakuten Securities says its notification emails contain no URLs and it will not ask for personal or login information over the phone. Be suspicious of messages offering urgent compensation or asking you to verify your account through a link.
Do I need to change my password or stop trading?
The announcement reviewed here does not impose a blanket password reset. It encourages passkey setup. Your next action should depend on your individual notice, account activity and whether you have disclosed credentials elsewhere.
Our Japanese article includes the author’s own notification: it listed branch/customer codes and the login ID. The author already used a passkey and chose to continue trading without changing the password or pausing trading solely because of that notice. This is a personal decision based on that account’s circumstances, not a recommendation for every customer.
- Review recent logins, orders, executions and withdrawals for activity you do not recognize.
- If you entered a password on a suspicious site, contact official support promptly and change compromised credentials through the genuine service.
- If a reused password was exposed elsewhere, replace it with a unique one and review other affected accounts.
- If you see unfamiliar activity, ask official support about available restrictions and the steps to investigate. Preserve evidence before making public claims.
What a passkey protects—and what it cannot prevent
A passkey uses cryptographic authentication tied to the legitimate service. It reduces the risk of handing a reusable password to a convincing imitation website. Follow the service’s own setup and recovery guidance, especially before replacing or losing a device.
A passkey does not stop an attacker from reading customer data already stored on a provider’s server if that server is compromised. Login protection and server-side data protection solve different problems. Even a customer with strong authentication can receive a breach notification and face targeted phishing.
Why a test environment can contain sensitive data
Test environments help developers check changes before deployment. If real customer records are copied there, those records still require protection. General controls include masked or synthetic test data, minimal retention, restricted access and audit logs. These are general security practices, not a finding about the specific weakness in this incident.
Frequently asked questions
Does knowing my login ID allow someone to trade? A login identifier is not the same as a complete set of authentication credentials. Nevertheless, use it as a reason to watch for targeted contact and review account activity.
Should I trust a caller who knows my name or bank details? Knowledge of personal information is not proof of identity. End the contact and reach the company through a trusted channel.
Where is the Japanese version? Read our Japanese notification and response guide. The public source is Rakuten Securities’ November 17 notice. Published November 18, 2026 (JST).








